How to get free SSL for your site with Cloudflare
Put HTTPS on your website for free in about 15 minutes. Most of it happens in a dashboard, not on your server.
A site without HTTPS gets a "Not secure" label in the browser. Visitors notice it, and so does Google. You don't have to pay to fix that. Cloudflare gives you an SSL certificate for free, and it renews on its own.
Here is the whole process, start to finish.
In short
- Cost: free
- Time: about 15 minutes of work, plus some waiting
- You need: a domain, and the login for the place you bought it
Before you start
Make sure you have these ready:
- A domain you own
- Access to your domain registrar (Namecheap, GoDaddy, Niagahoster, and so on)
- A website that already loads on that domain
01Add your domain to Cloudflare
Sign up at cloudflare.com, then add your domain. Type only the root, like yourdomain.com. No www, no https://.
When it asks you to choose a plan, pick Free. The SSL certificate is included.
02Check your DNS records
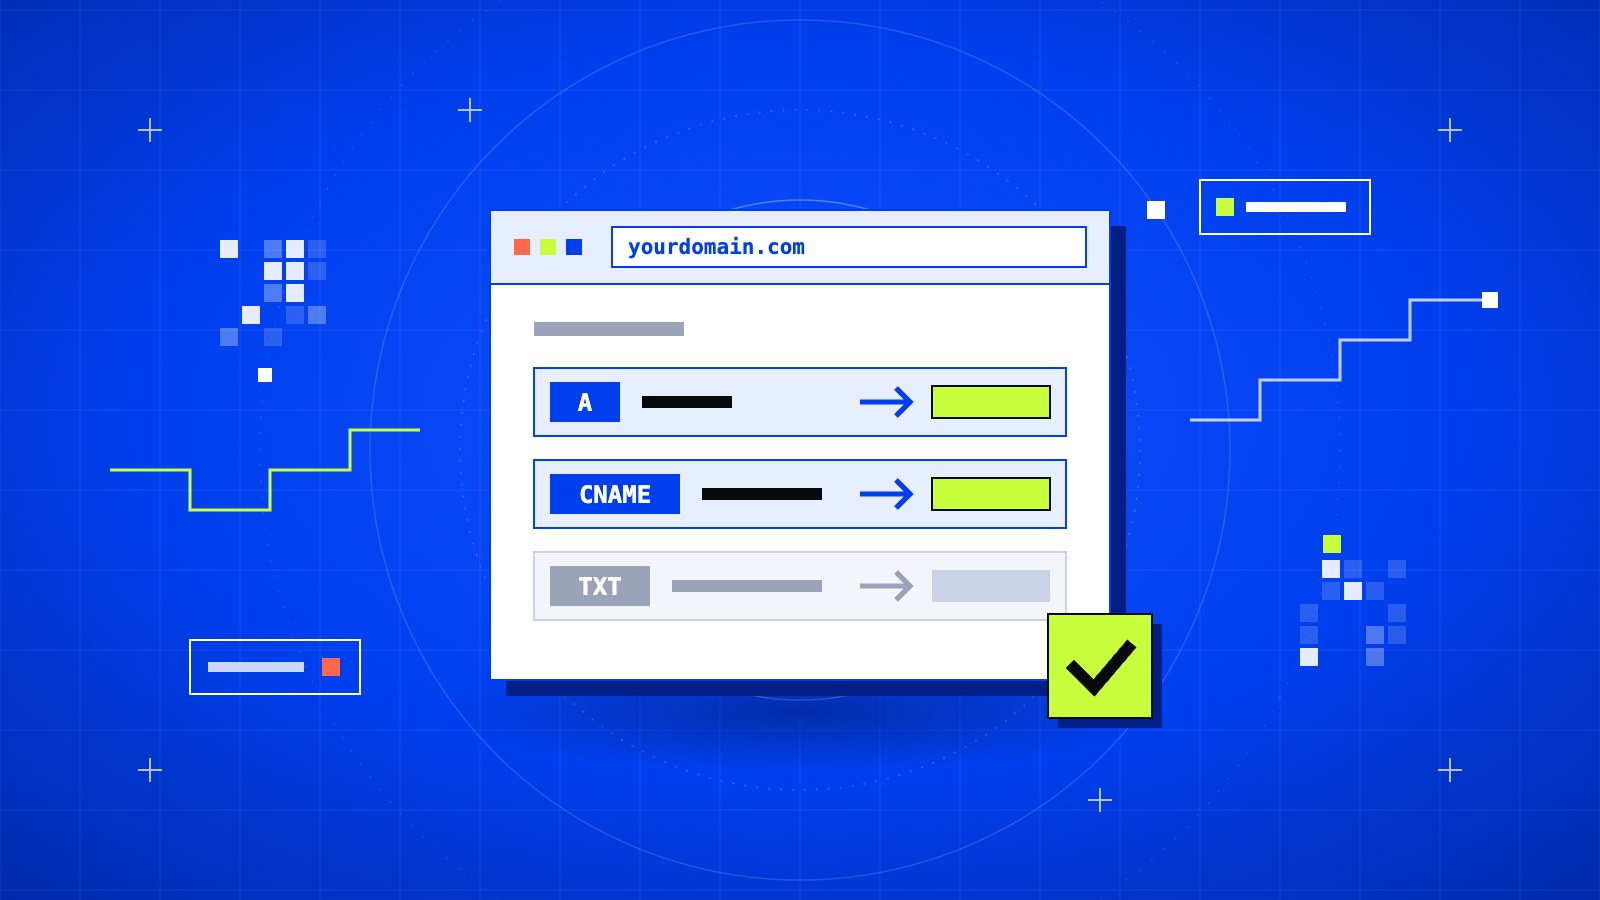
Cloudflare scans your current DNS records and shows them in a list. Compare that list with what you have at your current DNS provider. It usually finds everything, but check anyway. A missing record can take down part of your site or your email after the switch.
Then look at the Proxy status column:
- Website records (
A,AAAA, orCNAMEfor the root andwww) should be Proxied. That is the orange cloud. - Email records (
MX, and anything likemail) should stay DNS only. That is the grey cloud.
Note
Only proxied records get the free certificate. With a grey cloud, traffic skips Cloudflare and goes straight to your server.
03Change your nameservers
Cloudflare now gives you two nameservers. They look something like this:
ana.ns.cloudflare.com
bob.ns.cloudflare.com
Yours will have different names. Log in to your registrar, find the nameserver settings, and replace the old ones with these two. Save it.
Now you wait. It is often done in under an hour, but it can take up to 24. Cloudflare sends you an email when the domain is active.
Tip
Your site stays online during the switch. If the records from Step 2 are right, visitors won't notice anything.
04Let the certificate arrive
Once the domain is active, Cloudflare issues the certificate by itself. There is nothing to click.
You can watch it under SSL/TLS → Edge Certificates. The status goes from pending to Active, usually within 15 minutes, sometimes up to a day.
05Pick the right encryption mode
Go to SSL/TLS → Overview. This is the step people get wrong most often, so take a minute here.
- Flexible encrypts the trip from the visitor to Cloudflare only. Use it if your server has no certificate at all.
- Full encrypts the whole trip, and accepts any certificate on your server, even a self-signed one.
- Full (strict) encrypts the whole trip and checks that your server's certificate is valid. This is the one you want.
If your site runs on Vercel, Netlify, or most modern hosting, the server already has a valid certificate. Choose Full (strict).
Heads up
Don't use Flexible if your server already redirects to HTTPS. The two keep sending the visitor back and forth, and the browser gives up with a "too many redirects" error.
No certificate on your server yet? Create a free one under SSL/TLS → Origin Server → Create Certificate, install it on your server, then switch to Full (strict).
06Force HTTPS everywhere
Back in SSL/TLS → Edge Certificates, turn on two switches:
- Always Use HTTPS sends anyone who types
http://to the secure version. - Automatic HTTPS Rewrites fixes old
http://links to images and scripts inside your pages.
07Test it
Open https://yourdomain.com and look for the padlock. Then try the plain http:// address and check that it jumps to HTTPS.
If you like the terminal, this does the same check:
curl -I http://yourdomain.com
You should see 301 and a location line that starts with https://.
If something goes wrong
- "Too many redirects": the mode is Flexible while your server forces HTTPS. Switch to Full or Full (strict).
- No padlock, or a "mixed content" warning: some images or scripts still load over
http://. Turn on Automatic HTTPS Rewrites, or fix those links. - Certificate still pending after a day: check that your nameservers really point to Cloudflare and that the record is proxied.
- Error 526: you chose Full (strict), but the certificate on your server is invalid or expired.
- A deep subdomain is not covered: the free certificate covers
yourdomain.comand one level below it, likeshop.yourdomain.com. It does not covera.b.yourdomain.com.
That's it. The certificate renews by itself from here, so there is no expiry date to remember.
Still looking for a place to host the site? Vercel gives you free hosting and a live link in five minutes.